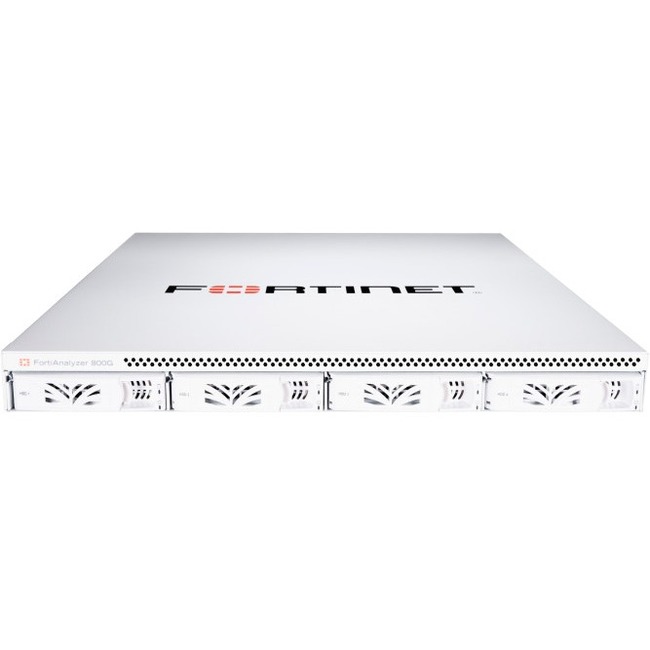
Fortinet FortiAnalyzer FAZ-800G Network Security/Firewall Appliance
Manufacturer: Fortinet, Inc
Mfr. Part: FAZ-800G
Web Filtering - 4 Port - 1000Base-T, 1000Base-X - Gigabit Ethernet - 4 x RJ-45 - 2 Total Expansion Slots - 50 Hz, 60 Hz - 1U - Rack-mountable
About This Product
Overview
Fortinet Security Fabric Visibility, Analytics, and Automation for the Modern Enterprise
FortiAnalyzer is a powerful log management, analytics, and reporting platform that provides organizations with a single console to manage, automate, orchestrate, and respond, enabling simplified security operations, proactive identification and remediation of risks, and complete visibility of the entire attack landscape. Integrated with the Fortinet Security Fabric, advanced threat detection capabilities, centralized security analytics, end-to-end security posture awareness and control, helps security teams identify and mitigate threats before a breach can occur.
Orchestrate security tools, people, and process for streamlined execution of tasks and workflows, incident analysis and response, and rapidly expedite threat detection, case creation and investigation, and mitigation and response.
Automate workflows and trigger actions with connectors, playbooks, and event handlers to accelerate your network security team's ability to respond to critical alerts, events, and service level agreement (SLA) for regulation and compliance.
Respond in real-time to network security attacks, vulnerabilities, and warnings of potential compromises, with threat intelligence, event correlation, monitoring, alerts and reporting for immediate tactical response and remediation.
FEATURE HIGHLIGHTS | Across Fortinet's Security Fabric | Incident Detection and Response | Centralized NOC/SOC Visibility for the Attack Surface
The FortiSOC view helps security and network operations teams protect network assets with correlated log and threat data and insights through actionable views with deep drill-down capabilities. Real-time notifications, reports, predefined or customized dashboards deliver single-pane visibility and actionable results. Utilize FortiAnalyzer workflow automation for simplified orchestration of security operations, management of threats, vulnerabilities, and incident response. Proactively investigate anomalies and threats through analysis of SIEM normalized logs in Threat Hunting view.
Event Management
Security teams can monitor and manage alerts and event logs from Fortinet devices, with events processed and correlated in a format that analysts can easily understand. Investigate suspicious traffic patterns and search using filters in predefined or custom event handlers to generate real-time notifications and monitoring for NOC and SOC operations, SD-WAN, SSL VPN, wireless, Shadow IT, IPS, network recon, FortiClient, and more.
- Supports network security and firewall appliance deployment by centralizing traffic inspection, policy enforcement, and access control
- 4 ports firewall supports basic network connectivity for compact or limited?scale deployments
- Supports policy?based inspection and controlled management of network traffic flows through threat protection firewall protection
- Supports Gigabit Ethernet to enable high-speed wired network connectivity for standard enterprise network environments
- Rack?mountable form factor allows secure and space?efficient installation within standard rack environments
- Supports USB interface to enable data transfer for compatible devices and supported operational use cases
Quick Specifications
- Product Line
- FortiAnalyzer
- Product Model
- FAZ-800G
- Product Type
- Network Security/Firewall Appliance
- Functionality
- Web Filtering
- Firewall Protection Supported
- Threat Protection Application Control Integrated Web Filtering Antivirus Content Filtering Email Content Filtering
- Total Number of Ports
- 4
- USB
- Yes
- Number of Network (RJ-45) Ports
- 4