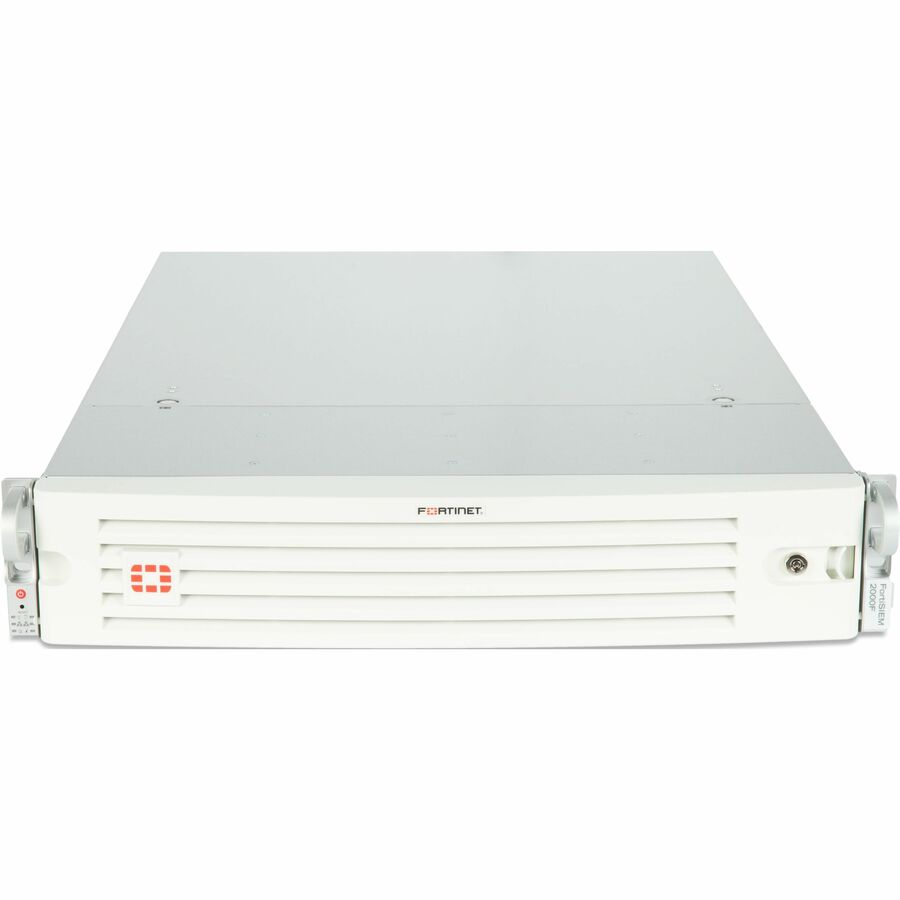
Fortinet FortiDDoS 2000F Network Security/Firewall Appliance
Wired - AI/ML Security - 40GBase-X, 10GBase-X - 40 Gigabit Ethernet - SSL, TLS 1.3, TLS - 8 Total Expansion Slots - 50 Hz, 60 Hz - 2U - Rack-mountable
About This Product
Overview
AI/ML Security and Deep Visibility
Distributed Denial of Service (DDoS) attacks remain a top threat to network security and have evolved in almost every way to do what they do best: shut down access to your vital online services.
Unlike intrusion and malware attacks, DDoS attackers have learned that they don't need to attack only end-point servers to shut you down. They attack any IP address that routes to your network: unused IP addresses, ISP link subnets, or Firewall/Proxy/WiFi Gateway public IP addresses.
CDN and DNS-based cloud mitigation cannot protect you from these attacks. What is the impact to your business if your users cannot reach cloud services because your firewall is DDoSed?
Sophisticated multi-vector and multi-layer DDoS attacks use direct and reflected packets where the spoofed, randomized source IP addresses are impossible to ACL. These attacks are increasingly common as Mirai-style code has morphed into many variants and has been commercialized by providers of "stresser" sites. Anyone can create large, anonymous attacks for a few dollars.
DDoS is not an everyday occurrence for security teams and they cannot be expected to understand the thousands of attack variants that target your network.
To combat these attacks, you need a solution that dynamically and automatically protects a large attack surface.
A Different and Better Approach to DDoS Attack Mitigation
FortiDDoS massively parallel machine-learning architecture delivers the fastest and most accurate DDoS attack mitigation available.
In place of pre-defined or subscription-based signatures to identify some attack patterns, FortiDDoS uses autonomous machine learning to build an adaptive baseline of normal activity from hundreds-of-thousands of parameters and then monitors traffic patterns against those baselines. Should an attack begin, FortiDDoS sees the deviation and immediately takes action to mitigate it, often from the first packet.
FortiDDoS monitors, responds, and reports on the mitigations it has performed, not attacks where your team or the vendor ERT/NoC must intervene.
- 100% packet inspection for Layer 3, 4, and 7 DDoS attack identification and mitigation, simultaneously monitoring hundreds of thousands of parameters - a massivelyparallel computing architecture
- 100% Machine Learning DDoS detection
- Completely invisible to attackers with no IP and no MAC addresses in the data path. FortiDDoS is not a routing or terminating Layer 3 device
- Continuous threat evaluation to minimize false positive detections
- Advanced DNS and NTP DDoS mitigation plus advanced DTLS and QUIC mitigation on F-Series
- Hybrid On-premise/Cloud mitigation available with Open Attack Signaling
Quick Specifications
- Product Line
- FortiDDoS
- Product Model
- 2000F
- Product Type
- Network Security/Firewall Appliance
- Functionality
- AI/ML Security
- Firewall Protection Supported
- Distributed Denial of Service (DDoS) Packet Inspection Deep Inspection Firewall Anomaly Detection Access Control Threat Protection
- Encryption Standard
- SSL TLS 1.3 TLS
- Data Link Protocols
- TCP/UDP HTTP
- Connectivity Technology
- Wired